
A fake job interview may seem like an unlikely starting point for a multibillion-dollar cyberattack. Yet that is the scenario described in Binance’s investigation into a security breach that resulted in approximately $6.34 billion in unauthorized cryptocurrency withdrawals on October 29, 2026. The incident highlights how attackers can exploit employee trust to reach systems holding enormous financial value.
How the Attackers Built Their Way In
Binance’s November 3 incident report describes a months-long, multi-stage operation. The company said an earlier software supply-chain compromise exposed information about an engineer and colleagues working on wallet infrastructure. A separate operation later targeted another employee through a fake recruitment process.
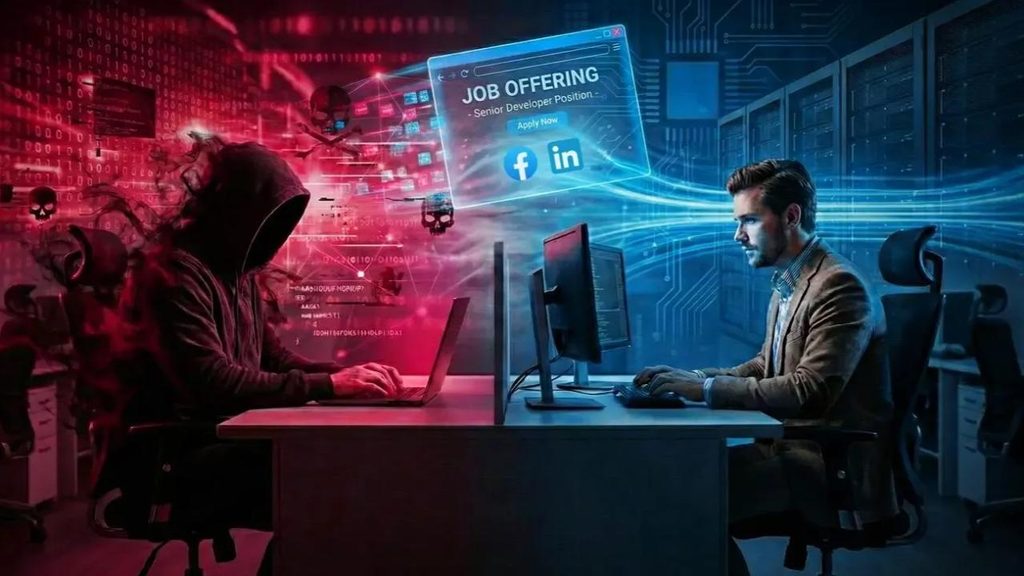
The supposed recruiters used video interviews and social media profiles to appear credible. During a later interview, the employee was asked to download a technical assignment. Binance said the code repository contained malware that compromised the employee’s work computer and helped attackers gain access to internal systems.
The operation reportedly escalated through compromised devices, stolen credentials and internal tools. Attackers eventually reached wallet-related infrastructure and triggered unauthorized transactions. The Binance incident report says the breach involved more than a simple phishing message.
Why the $6.3 Billion Theft Matters
The FBI attributed the theft to North Korea and identified the activity as TraderTraitor. The attribution is significant because North Korean-linked cyber operations have repeatedly targeted cryptocurrency businesses and digital assets.
Reuters reported that most of the stolen cryptocurrency moved within roughly 20 minutes. The scale and speed of the withdrawals demonstrate how quickly a compromise of privileged access can become a financial crisis. The Reuters investigation also described efforts by blockchain firms and asset issuers to freeze portions of the stolen funds.
Binance said it would absorb the financial impact rather than pass the loss to customers. In its November 3 update, the company reported that approximately 98% of affected token assets had been replenished. Those figures come from the exchange and remain subject to its ongoing review. The company’s earlier response outlined its initial containment and recovery measures.
Corporate Security Must Look Beyond Passwords
The breach offers a warning to businesses across industries. Security programs cannot focus only on firewalls, password strength and suspicious email attachments. Attackers may use recruitment platforms, messaging apps, software downloads and convincing professional identities to build trust before delivering malware.
The Washington Post’s reporting describes how the fake interview became part of the intrusion. Meanwhile, the FBI’s 2025 Internet Crime Report shows the wider financial scale of cyber-enabled fraud in the United States.
Companies should verify external recruiters and contractors, restrict software installation privileges, monitor unusual device activity and require strong approval controls for sensitive transactions. Security teams should also rehearse how to revoke credentials and halt suspicious operations quickly.
A Human Trust Problem With Financial Consequences
Binance’s breach shows that sophisticated cyberattacks do not always begin with a dramatic technical exploit. They can start with a credible conversation and an ordinary-looking work task. As companies adopt more connected tools and AI-assisted workflows, employee awareness and tightly controlled access remain essential parts of cybersecurity.
The central lesson is clear: corporate security must protect both digital infrastructure and the people trusted to operate it.
#Cybersecurity #Binance #SocialEngineering #CryptoSecurity #CyberAttack #DataProtection #TechnologyNews #DigitalRisk #AIandCybersecurity